
Enterprise Technology & Cybersecurity Executive
Building the strategy, teams, and security posture that let organizations move faster with less risk.
Areas of Expertise
Four disciplines I bring to every engagement.
Security & Risk Leadership
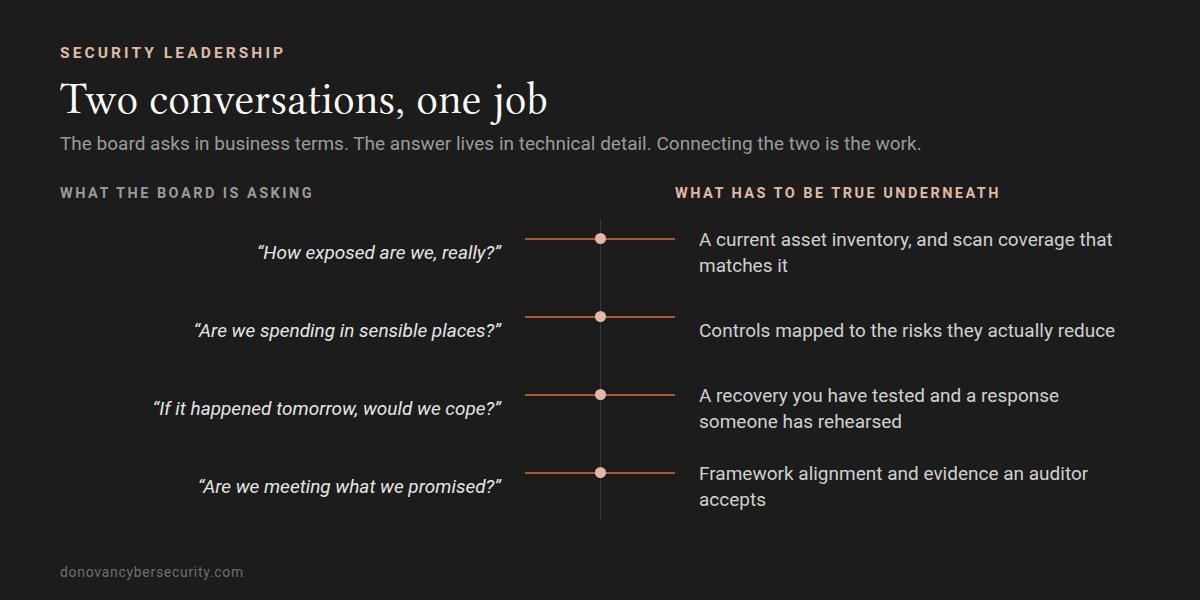
Enterprise security strategy, program development, governance, and translating technical risk into board-level decisions.
Enterprise Infrastructure & Cloud
Modernization, cloud strategy, identity, and operational resilience across distributed operations.
AI Governance
Policies and frameworks that let organizations adopt AI safely and responsibly.
Compliance & Assurance
Aligning security programs with regulatory, audit, and framework requirements (NIST, ISO, CIS).
At a Glance
25+
Years leading enterprise technology & security
$4M+
Annual technology budgets managed
19
Locations supported across distributed operations
CISSP · CCISO
Certified since 2010
Director of Compliance, regional InfraGard chapter — an FBI–private sector partnership.
Let’s talk about where your program stands
A 30-minute conversation is usually enough to identify the two or three things worth fixing first.